The sign-in protects your bank matching, your customer list and your tax returns, so give it ten minutes. Security isn’t a paid add-on here. Charging extra for an account being hard to break into has always struck us as a strange way to price software.
What you can do
- Turn on two-factor authentication with any authenticator app.
- Decide how long a session can sit idle before it signs itself out, for the whole company.
- Issue API keys for your own scripts and tools.
- Review login history: when, from where, and how.
- Reset a forgotten password by email, on a link that expires.
- Close your account through a defined process rather than a support request.
How it works in practice
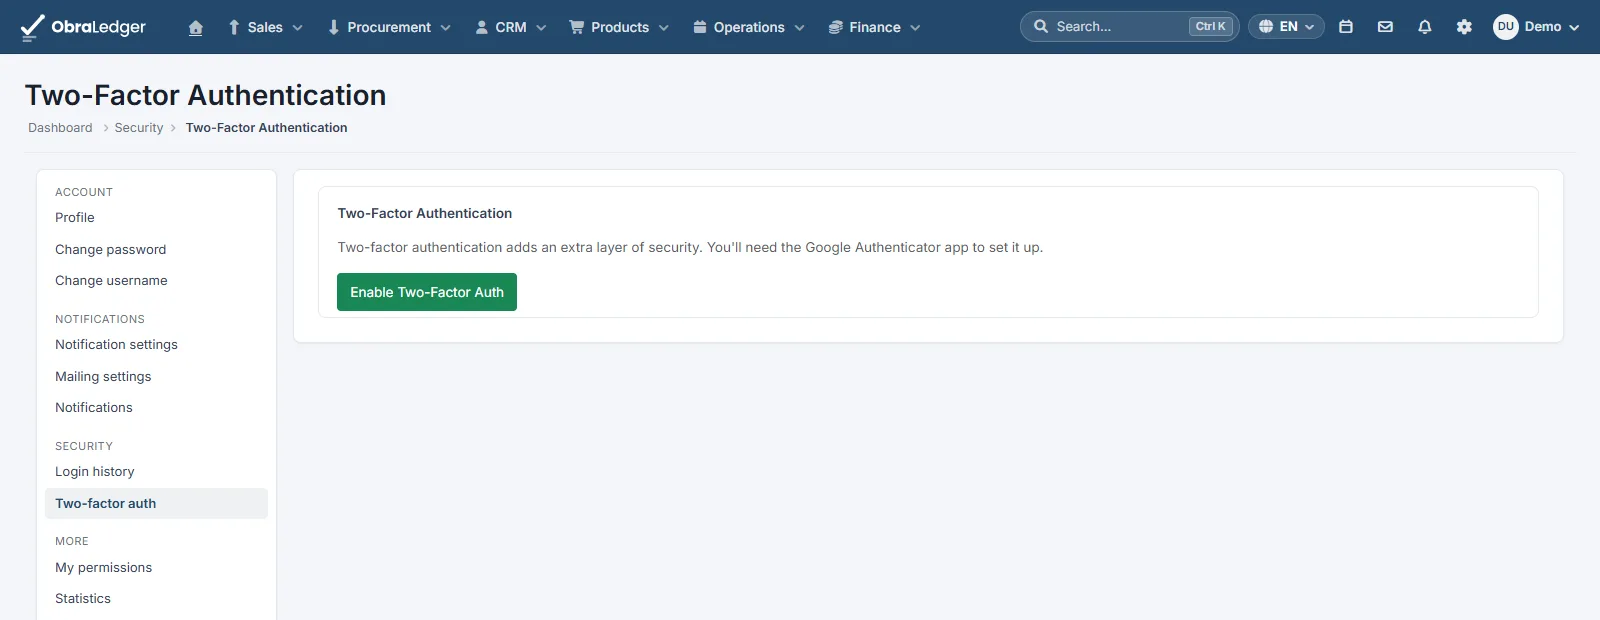
Turn on two-factor authentication (your profile → Sign-in & security). Scan the code with whichever authenticator app you already use, then confirm with a code from it. That confirmation step is required, so an account can’t end up locked behind a code nobody can generate. After that, signing in asks for the app’s six digits once you’ve entered your password.
Set the idle timeout for everyone else (Settings → Security → Security Policy). It applies to every user in the company, and it’s short by default.
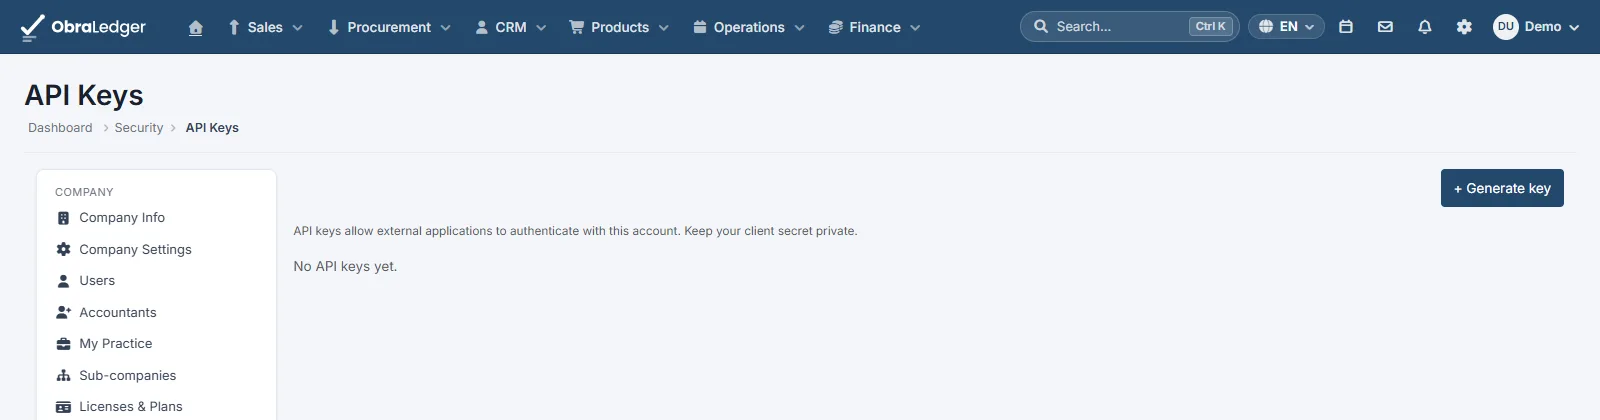
Issue an API key when something needs to talk to the system (Settings → Security → API Keys). Only a company administrator can issue one. You choose what it may do - read contacts, change products - and it can never do more than you can. Treat it like a password, and remove it when whatever used it is retired. Building against the API? How keys and scopes work has the detail.
Check the login history if something feels wrong. Every sign-in is recorded with its time, the address it came from and the country that resolves to. It’s the first place to look when you suspect a shared password, and the quickest way to confirm nothing untoward happened.
If you forget your password, use the Forgot password? link on the sign-in page. The reset link is emailed to you, lasts an hour, and works once: following it a second time, or forwarding the mail to somebody, gets them nowhere. You can ask for a new link once a minute.
Closing the account is a process with steps (Settings → Security → Security Policy, in its danger zone, for company administrators), not an email to support: the request, a confirmation, and a record that it happened. You’re asked why, which you’re free to ignore. Take your exports first - see getting your data in and out.
Good to know
- Two-factor authentication is per person, not per company. You can require it of yourself right now. Getting a colleague to turn theirs on is a conversation rather than a setting, and if everyone in your company handles money, it’s a conversation worth having.
- Authenticator apps only. Codes by email or SMS aren’t offered. Text messages in particular are the weakest common form of two-factor, and offering a weak option next to a strong one mostly gets the weak one chosen.
- Keep your recovery method. If you lose the device your authenticator lives on and have no backup, getting back in becomes a support matter with identity checks. Most authenticator apps offer a backup, so use it.
- Give a key only what the job needs. A reporting tool needs to read invoices, not create them. Narrow a key when you make it, and make a second one for the next job.
- Permissions are what actually limit people, and they’re per company. See users, roles and companies. Sign-in security protects the account; roles decide what that account may do once it’s inside.
- A password reset says the same thing whether or not you have an account. The page confirms the mail was sent either way, because a message saying “no account with that email” would tell anyone who asked which addresses are worth attacking. If nothing arrives, check the address you typed.
- Sign up on an address you’ll still have next year. Throwaway mailboxes are turned away at registration, and the message says why. Everything that gets an account back - the verification link, and every password reset after it - arrives by email, so a mailbox anybody can open and nobody owns is an account nobody can recover.
- Signing out everywhere isn’t the same as changing your password. If you think a password has leaked, change it. That’s what stops somebody who already has it.